
Behind the Scenes at Shock Media During PHP2Shell
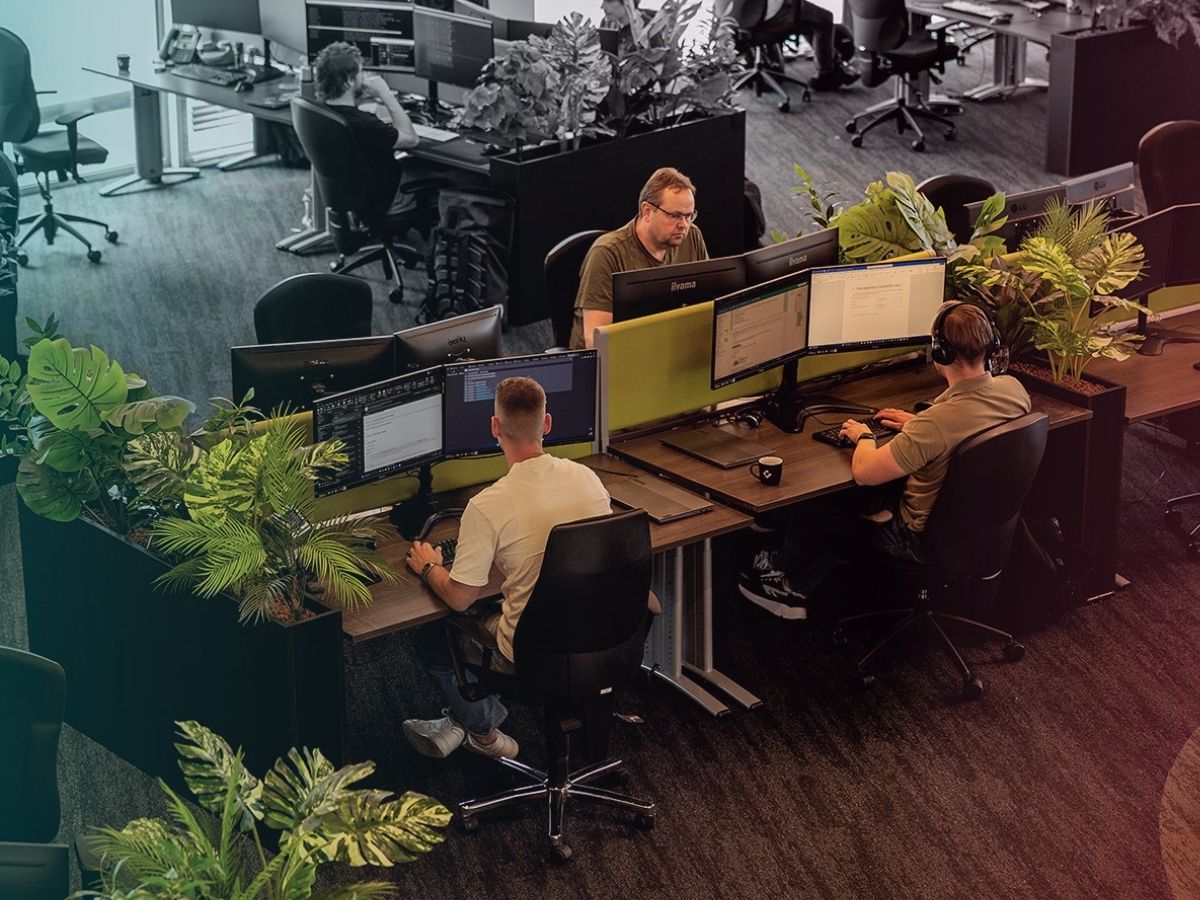
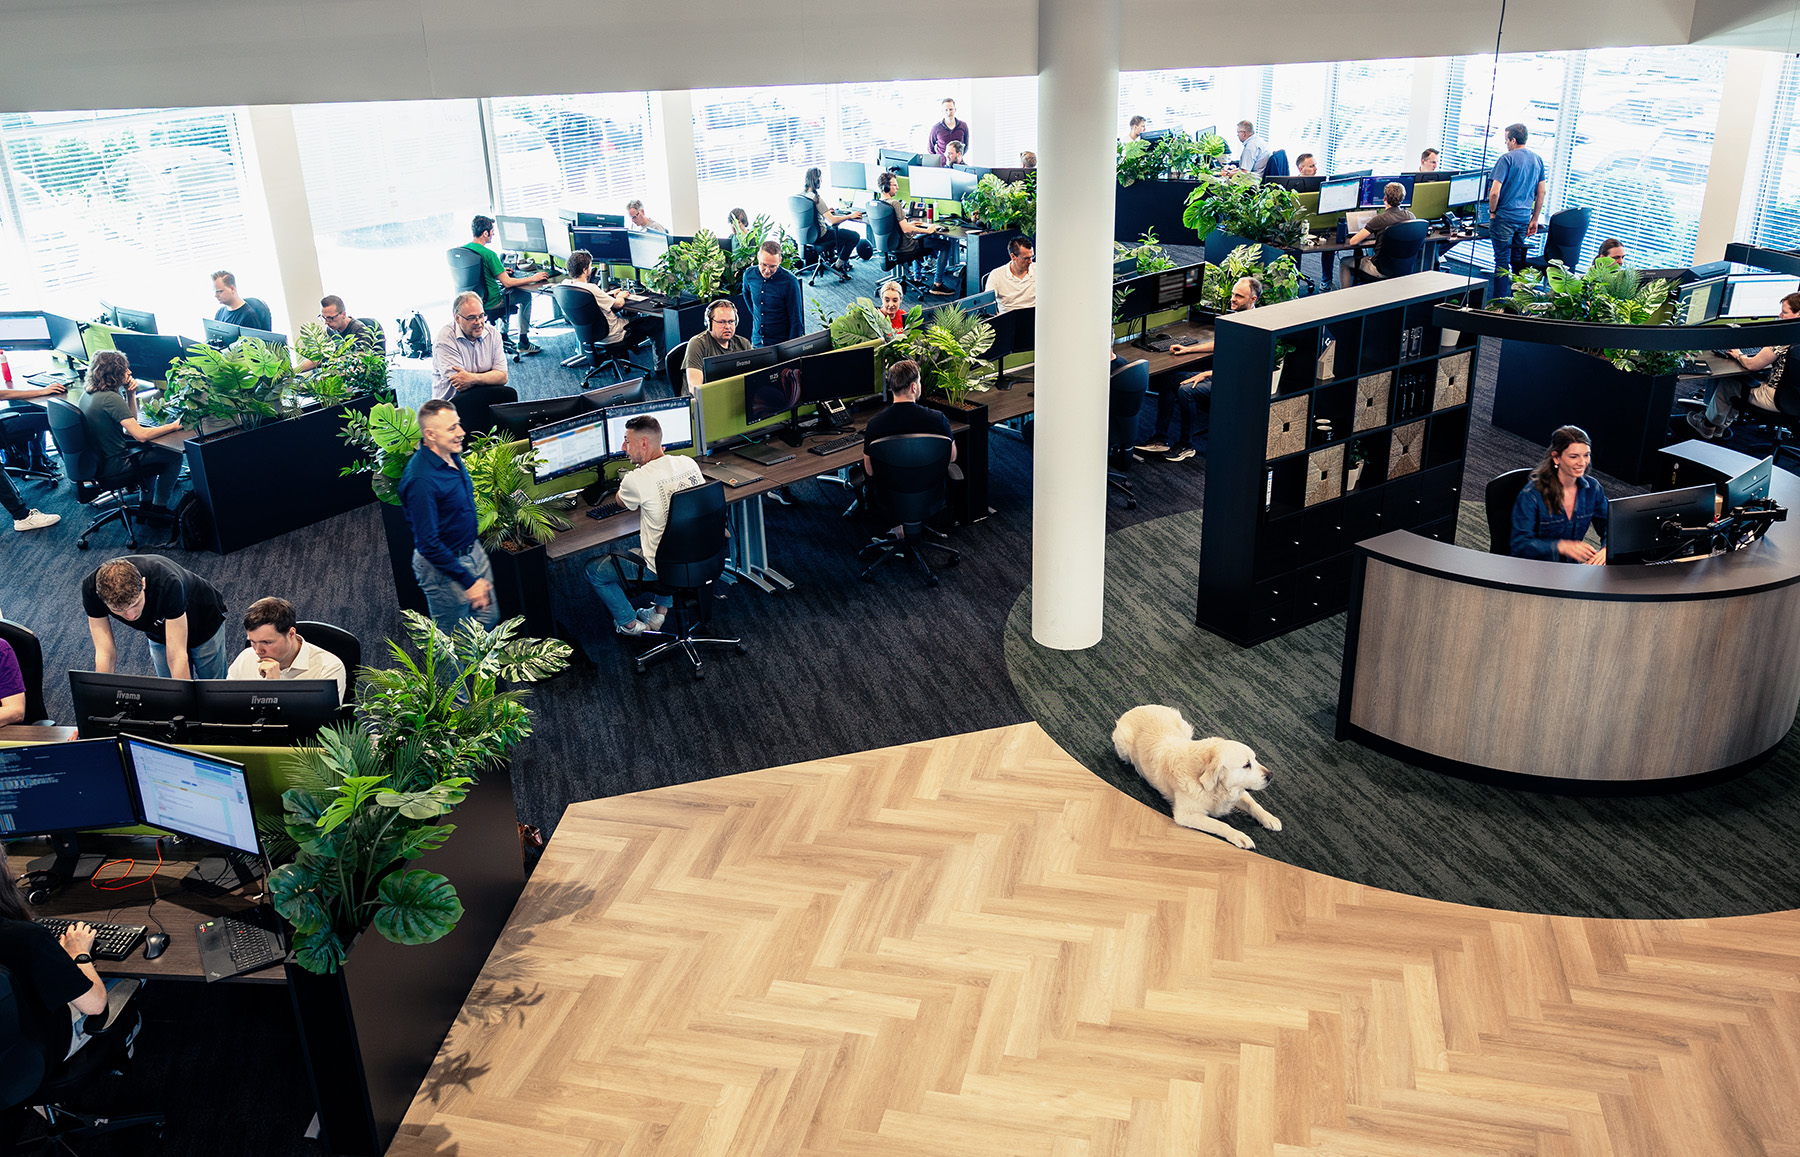
Thousands of websites and applications had to be taken offline as a precaution. On Wednesday, 21 October 2026, PHP2Shell was the main focus at Shock Media. A critical vulnerability in PHP had been discovered, but no patch was available yet. There was no time to lose. As the threat continued to grow, our colleagues worked tirelessly behind the scenes to implement mitigating measures and minimise the risks. What happened that day, what decisions were made, and what was it like at the Shock Media office?
A critical vulnerability calls for immediate action
On Tuesday, 20 October 2026, PHP announced an urgent security update scheduled for the following day. At the same time, technical details of the vulnerabilities being addressed were leaked online by others, prompting attackers to quickly begin their first attempts to exploit PHP applications.
On Wednesday, 21 October 2026, several security companies reported active cyberattacks exploiting the PHP2Shell vulnerability. The news spread rapidly, and the urgency of the situation became increasingly clear. PHP is widely used, meaning websites and applications around the world were at risk of being exploited by malicious actors.
We immediately published an alert on our status page: shockmedia.info, at 08.55 AM. Our Incident Response Team also came together to assess the situation. Our security specialists and engineers worked to identify the potential impact. With a vulnerability like this, it is not just about fixing the security flaw, but also about preventing exploitation while no definitive solution is available. Through our security monitoring and Active Response services, we immediately implemented mitigating measures to reduce the risks.
What is PHP2Shell and why is it so critical?
PHP2Shell (known as CVE-2026-109618 and CVE-2026-109619) is a critical vulnerability deep within the PHP core, specifically affecting the handling of multipart/form-data and upload progress. PHP is the most widely used programming language on the web, meaning an attack could have serious consequences.
An attacker can exploit the vulnerability to execute arbitrary code remotely, also known as Remote Code Execution (RCE). This can give them access to applications and data, including customer information, patient records and other sensitive data that must not fall into the wrong hands. An attacker could view, distribute, manipulate or delete this data.
With a CVSS score of 9.2 out of 10, the vulnerability was classified as critical. The combination of the vulnerability and reports of active exploitation made immediate action essential. Waiting was simply not an option.
The impact was enormous: all hands on deck
The first customer enquiries came in at around 8:30 a.m. and quickly increased in number. Our team was already busy implementing precautionary measures. Within no time, our phone lines were overwhelmed. Due to the volume of incoming calls, we could no longer answer all enquiries effectively. We therefore decided to temporarily disable phone support so our colleagues could focus entirely on the tasks that mattered most at that moment. In the meantime, customers received updates through our status page.
Colleagues from all departments stepped in to help answer incoming tickets, call customers where necessary and ensure urgent requests reached our system administrators through emergency tickets. This allowed our engineers to focus on the technical measures while ensuring customers received as much support and information as possible.
A patch was not immediately available to fix the vulnerability. PHP had announced that it would be released at 4:00 p.m., but waiting was not an option. We also received a large number of requests to temporarily make websites inaccessible. After careful consideration and monitoring, we ultimately decided to temporarily disable PHP. As a result, all websites and applications using PHP were taken offline as a precaution until the security patch became available.
The impact was significant: websites belonging to municipalities, government organisations, schools, healthcare institutions and many other organisations temporarily went offline.
It was a drastic measure, but everyone agreed: the security and privacy of our customers come first. Our customers understood why this was necessary. At that moment, protecting their environments and their customers’ data was more important than availability.
Making careful decisions under pressure
In our earlier article about vulnerability management in the age of AI, we explained why waiting until the next scheduled maintenance window is not always an option. When dealing with a high-risk vulnerability, our security specialists and engineers immediately assess which measures are required. PHP2Shell demonstrated just how important this approach is.
Assessing a vulnerability, identifying its potential impact and determining the necessary measures require technical expertise, clear procedures and short communication lines. But this situation called for more than just a technical solution.
At the same time, we needed to keep our customers informed about what was happening. Everyone wanted clarity. How serious was the risk, and what did it mean for their environment? We informed our customers by email, addressing the most frequently asked questions. We also kept them regularly updated on the latest developments through our status page.
Behind the scenes, our colleagues continued working with full focus. Our office manager made sure everyone had enough food and drinks. A small gesture, but one that was greatly appreciated. On a day like this, it is not just about technology. Teamwork, communication and trust are just as important.
Stronger together!
As soon as the official patches became available, we rolled them out across our entire infrastructure and PHP was made available again. Our colleagues continued working late into the evening to secure our customers’ environments and restore services.
PHP2Shell was an exceptional situation that demanded a great deal from both our team and our customers. We have extensive procedures in place for situations like these, and this incident demonstrated just how important they are. Being prepared allowed us to make decisions quickly and respond effectively.
Thank you to our colleagues and customers
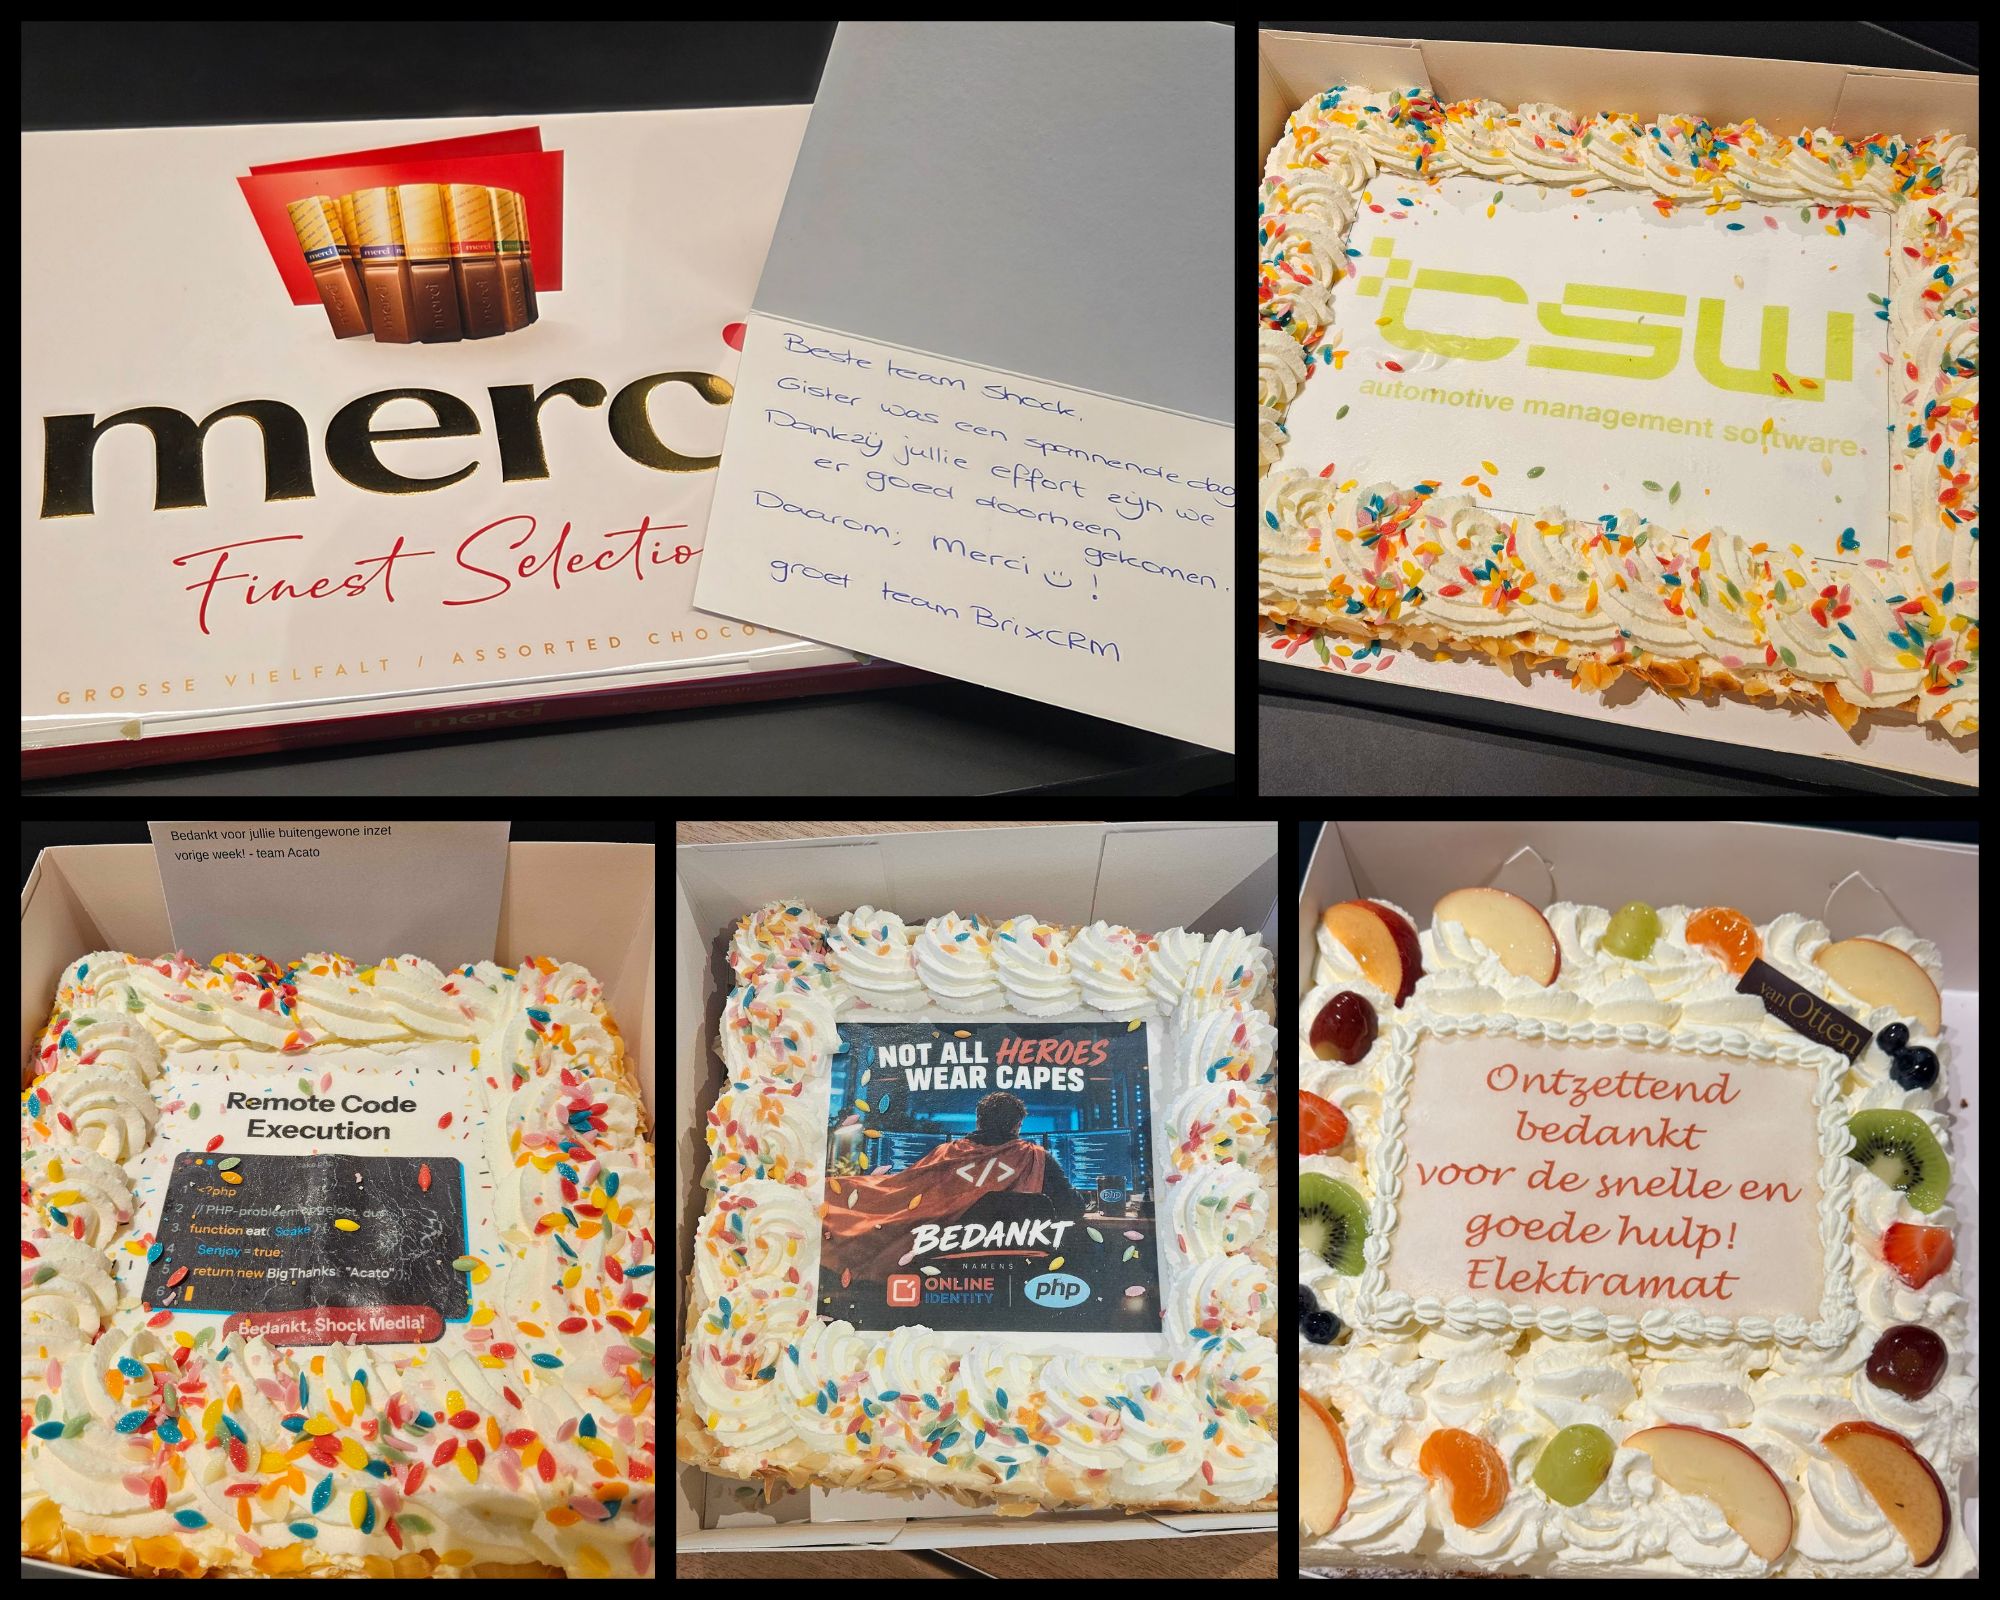
In the days following the incident, we received many kind messages, compliments and thank-you gifts in the form of delicious treats and gifts. We truly appreciate this! We would also like to take this opportunity to thank our customers for their understanding, trust and patience on a day when everyone faced difficult decisions.
Thank you once again!