
The number of published vulnerabilities is growing faster than ever, while the time between a vulnerability becoming known and it actually being exploited is getting shorter and shorter. For organizations responsible for business-critical environments, this means that traditional, scheduled patch management is no longer sufficient. In this article, we explain how the threat is evolving and how we at Shock Media have structured our approach accordingly.
For a long time, patch management was known as a recurring, predictable process: vulnerabilities were collected, prioritized and resolved within a fixed maintenance window. That approach was sufficient for many years. By now, however, this model is outdated, which requires a different way of working.
The figures: more vulnerabilities, less time to respond
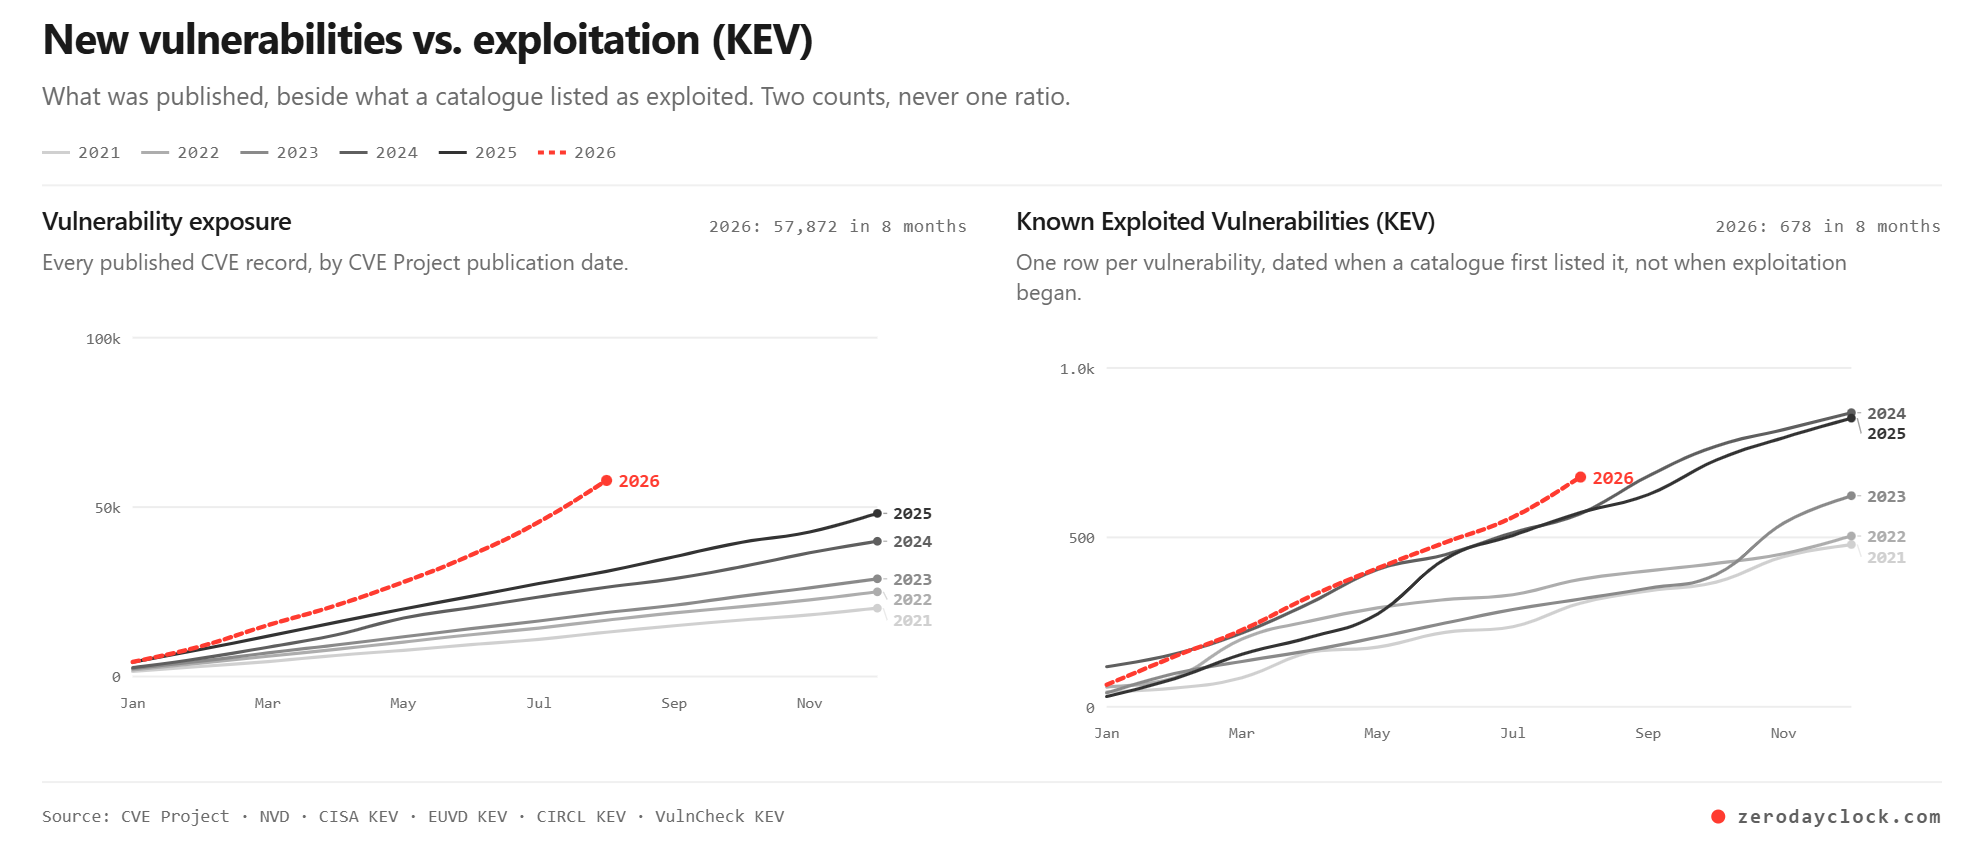
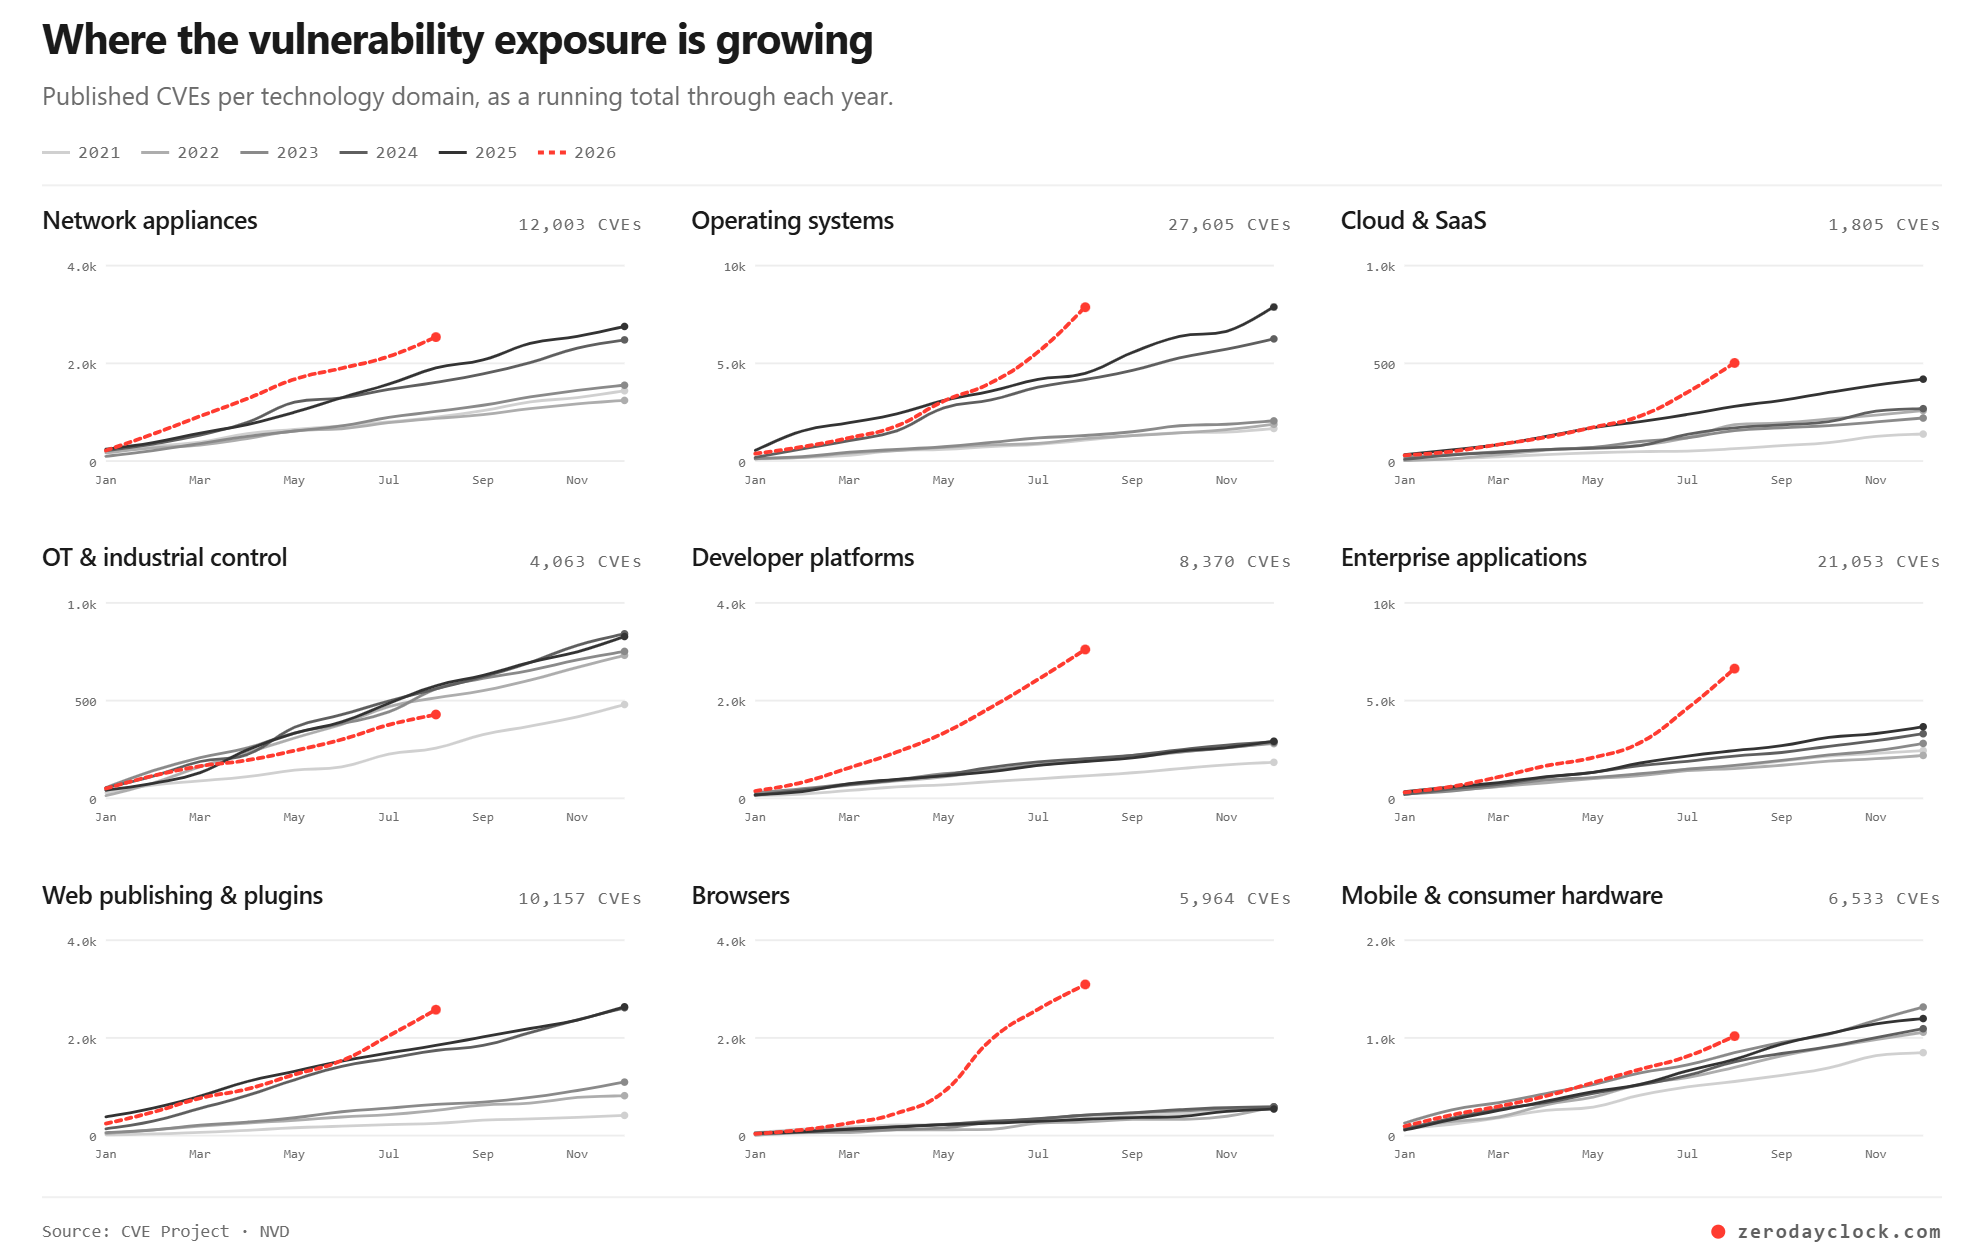
The scale of the problem has increased significantly in recent years. In 2025, more than 48,000 new Common Vulnerabilities and Exposures (CVEs) were published. A CVE is a unique identification number that allows security specialists worldwide to know exactly which specific vulnerability is being referred to. In 2025, this represents an increase of more than twenty percent compared to 2024, which was already a record-breaking year. This amounts to more than 130 new vulnerabilities per day. The first half of 2026 shows a similar, further accelerating trend, with a production rate of almost one new CVE every seven minutes.
At the same time, the time between the publication of a vulnerability and the first active exploitation has decreased drastically. Whereas a few years ago this was still measured in weeks to months, multiple studies now report that vulnerabilities are sometimes actively exploited within just a few hours of publication, partly driven by automated scanning and AI-assisted exploit development. In some cases, a vulnerability is even exploited before an official patch is available.
How do we deal with this at Shock Media?
The security of the Managed Hosting and Cloud Infrastructure that we manage for our customers is, of course, our highest priority. Continuously assessing and patching vulnerabilities is therefore an important part of our work as a Managed Hoster. We translate developments in the field of AI and vulnerabilities into an approach that does not rely on a single measure, but on a combination of structural processes and targeted action when needed.
Naturally, this starts with highly detailed insight into all software running on the systems we manage. Based on this insight, we have the capacity to perform packages and minor updates automatically at a high frequency, so that vulnerabilities are resolved immediately and do not accumulate between maintenance moments. We can roll out many updates without any noticeable impact, but some updates can have an impact. For these, we have an extensive update strategy, whereby updates that may affect our customers’ services are implemented within scheduled maintenance windows and in coordination with our customers.
It is also, of course, important to know what needs to be fixed. That is why we continuously collect and assess information from various sources about new vulnerabilities and CVEs. For each vulnerability, our security specialists and engineers conduct a risk assessment and impact analysis to determine how urgently patches or other mitigating measures need to be implemented. When this assessment shows that a vulnerability poses a high risk, or is actively being exploited, for example, we do not wait for the next maintenance window: we carry out emergency maintenance immediately to mitigate the vulnerability.
Our vigilance does not stop at patching alone. We block a great deal of abuse through our Active Response service. In addition, we actively monitor our environments for signs of exploitation of vulnerabilities that are being abused, and we continuously perform vulnerability scans so that anomalies and outstanding vulnerabilities are quickly identified and resolved. Clear coordination with our customers is an integral part of all this. Active software versions, implemented updates and maintenance moments are always visible through our customer portal, and we communicate clearly and in a timely manner about scheduled maintenance and emergency maintenance. This is how we keep your services at Shock Media secure!
Patching in the future
The trend of more vulnerabilities and a shorter Time to Exploit does not appear to be reversing anytime soon. As attackers increasingly use automated tools and AI to find and exploit vulnerabilities, defense will also need to become more automated and faster.
A periodic and manual update process has long been insufficient. In today’s world, a continuous and largely automated process is needed, in which relevant vulnerabilities can be identified, assessed and resolved within a very short period of time. A reliable Managed Hosting partner is therefore also an important link in the security of your business-critical applications and data.
More information?
Would you like to know how we have structured patch and vulnerability management for your environment, or do you have questions about a specific vulnerability such as wp2shell? Take a look at our Trustcenter page within our customer portal or feel free to contact us. We are happy to think along with you!