
On August 15, 2026, the Cybersecurity Act entered into force, the Dutch implementation of the European NIS2 Directive. Between 8,000 and 10,000 organizations in the Netherlands are directly subject to the new obligations. In addition, it also has an immediate impact on the suppliers and service providers of these organizations. For many companies, the question is no longer whether they will be affected, but how quickly they can demonstrate that their security is in order.
What is the Cybersecurity Act (NIS2)?
The Cybersecurity Act (Cbw) is the Dutch implementation of the European NIS2 Directive and replaces the current Network and Information Systems Security Act (Wbni). We live in a time in which we are dealing with many cyber threats. The aim of this law is therefore to strengthen the digital resilience of critical and important sectors in the Netherlands.
Who does the law apply to?
The Cybersecurity Act is intended for organizations in sectors that are classified as essential or important.
Very critical:
|
Other critical sectors
|
Is your organization not directly covered by these sectors? You may still be affected by the law, namely as a supplier or chain partner of an organization that is covered by it. It does not only depend on the sector, but also on factors such as the size of the organization and the specific statutory criteria.
Size requirements
Basically, the Cybersecurity Act applies to organizations with 50 or more employees. Organizations with fewer than 50 employees may also fall under the Cybersecurity Act if they operate in a designated sector and have both an annual turnover and a balance sheet total of more than €10 million.
Large, directly designated organizations are also required to assess and manage the digital security of their suppliers.
What do you concretely need to do?
As of the effective date, a number of important obligations apply:
- Registration obligation: organizations covered by the law must register with the National Cyber Security Centre via mijn.ncsc.nl.
- Duty of care: take appropriate technical and organizational measures to manage cyber risks, with explicit management responsibility.
- Incident reporting obligation: a significant cyber incident must be reported within 24 hours of discovery, with a follow-up notification within 72 hours and a full final report within 30 days.
- Supply chain responsibility: identify and manage risks at suppliers.
What does this mean for the supply chain?
Even if you are not directly subject to the Cybersecurity Act yourself, you may still be affected by customers who are and who ask you questions about your digital security as a supplier. If you cannot demonstrate that your security is in order, you risk losing business opportunities. Cybersecurity is becoming increasingly important, and companies are increasingly seeing it as a prerequisite for doing business.
How Shock Media supports this
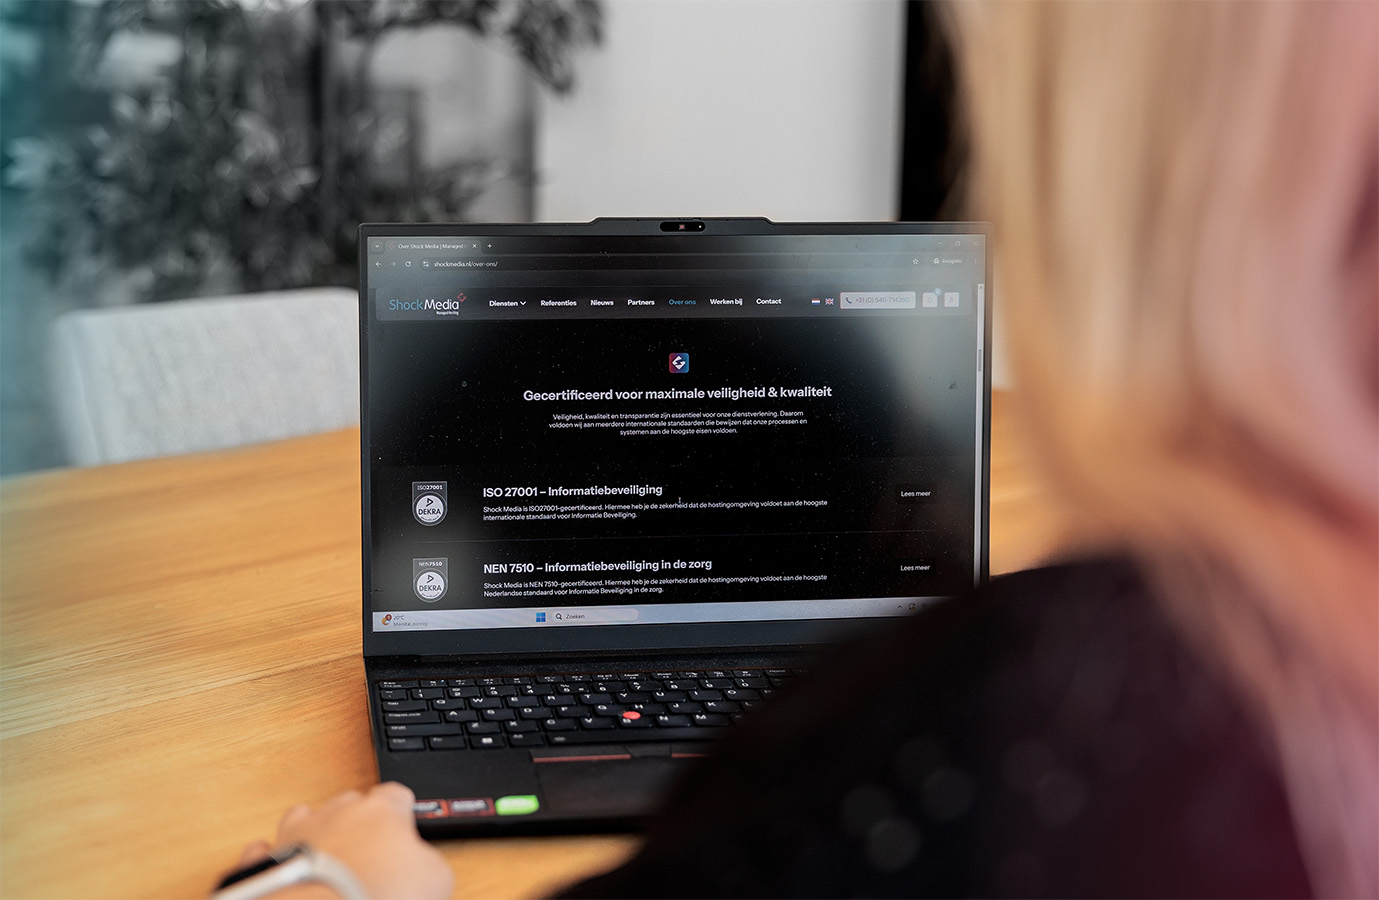
Shock Media has been certified for many years according to ISO 27001, NEN 7510, and ISO 9001. We report in accordance with SOC 2 and ISAE 3402 Type II. These certifications provide ongoing evidence of how we manage information security, quality, and compliance.
For customers who are themselves subject to the law, or who are questioned by their own customers about the security of their supply chain, hosting business-critical applications with Shock Media means that they can directly fulfill an important part of this demonstrability.
What does this mean for our customers?
Shock Media customers can demonstrate to regulators, auditors, and end customers that their infrastructure meets high security standards. This is directly relevant if an organization itself falls under the Cybersecurity Act, or if it must demonstrate as a supplier that its digital security is in order.
Would you like to know what the Cybersecurity Act specifically means for your environment? Or would you like to host your business-critical applications with us? Then contact us for a no-obligation consultation.